Team · 25+ professionals
The people who do the work.
25+ certified security professionals working from Pakistan and the United States. Offensive specialists, detection engineers, forensic analysts and risk advisors. Everyone below is named, because the people at the keyboard are what you are choosing when you choose a testing firm.
The bench · 14 named
-
 Daniyal Nasir
Co-Founder and Principal Consultant
Sets engagement standards and reviews delivery. Reached HackerOne’s all-time Top 100.
-
 Taha Khan
Co-Founder and Senior Consultant
Web and API penetration testing, authorisation boundaries and multi-tenant isolation.
-
 Huzaifa Jawaid
Cyber Security Analyst
Detection engineering, alert triage and threat hunting across client estates.
-
 Usama Jawed
Head of Application Security
Web and API engagements, authenticated multi-role testing, secure code review.
-
 Muhammad Khizer Javed
Cyber Security Manager
Engagement delivery and vulnerability research. Conference speaker on bug bounty methodology.
-
 Anees Khan
Lead Penetration Tester
Web, API and mobile testing; business logic and chained exploitation.
-
 Babar Akhunzada
Cybersecurity Advisor
Security strategy, programme design and advisory for platform and fintech clients.
-
 Muhammad Qasim Munir
Senior Cybersecurity Consultant
Enterprise assessments, cloud configuration review and compliance-mapped testing.
-
 Hisham Mir
Risk Advisor
Risk assessment, control effectiveness review and ISMS-aligned reporting.
-
 Usama Arshad
Senior VAPT Engineer
Vulnerability assessment and penetration testing across web, network and mobile estates.
-
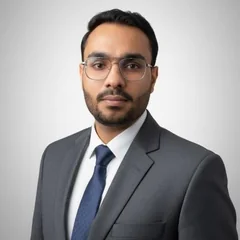 Mubassir Kamdar
Senior Cyber Security Consultant
Application and infrastructure testing, vulnerability research and disclosure.
-
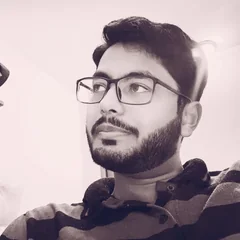 Arslan Mazhar
Senior Network Security Engineer
Internal and external network testing, Active Directory attack paths, segmentation validation.
-
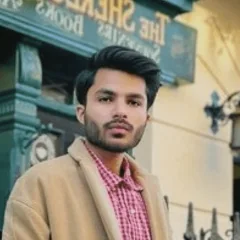 Muhammad Osama Asghar
Application Security Engineer
Application testing, secure development review and remediation support.
-
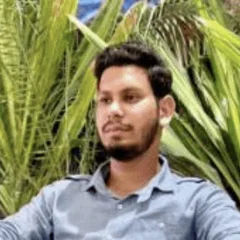 Khurram Saeed
Vulnerability Management Analyst
Continuous vulnerability tracking, triage, retest verification and closure evidence.
The testers assigned to your engagement are named during scoping and held to contractually. You are not handed a pool, and a senior name does not go on a report a junior wrote.
How the practice is structured
Specialists, not generalists.
Offensive testing, detection and forensics are separate disciplines. We staff them separately rather than asking one person to be adequate at all three.
| Role | Focus |
|---|---|
| Principal Consultant | Engagement standards, methodology, delivery review and escalation on every engagement. |
| Senior penetration testers | Web, API, mobile and cloud engagements; authenticated multi-role testing and chained exploitation. |
| Network and infrastructure specialists | Internal and external network testing, Active Directory attack paths, segmentation validation. |
| Red team operators | Objective-based adversary simulation, payload development, detection evasion and purple-team replay. |
| Detection engineers and analysts | Threat hunting, SIEM detection engineering, alert triage and threat intelligence translation. |
| Forensics and malware analysts | Incident response, disk and memory forensics, reverse engineering and indicator extraction. |
| Risk and assurance | Control effectiveness review, engineer-grade and auditor-grade reporting, retest attestation. |
Leadership · Accepting work
Leadership
-
Co-Founder2018
Daniyal Nasir
Co-Founder and Principal Consultant
Over a decade in offensive security, from bug bounty research in 2014 to setting the engagement standards every tester here works to. Reached the Top 100 on HackerOne’s all-time leaderboard, with acknowledgements from Microsoft, GitHub, Intel, SAP, Booking.com, Docker and the U.S. Department of Defense. Holds OSCP, LPT Master, CPENT, CISA and CISM.
-
Co-Founder2018
Taha Khan
Co-Founder and Senior Consultant
-48 years building the firm’s application security practice, which is where most of its engagements sit. Works across web and API testing, with a focus on authorisation boundaries and multi-tenant isolation — the flaws that let one account reach another tenant’s data, and the ones automated scanning consistently misses. Holds OSCP, CEH and CompTIA Security+.
Certifications held across the team
- OffSec Certified Professional (OSCP)
- OffSec Web Expert (OSWE)
- CREST certified (CREST)
- Licensed Penetration Tester (Master) (LPT Master)
- Certified Penetration Testing Professional (CPENT)
- Certified Ethical Hacker (v12) (CEH v12)
- Practical Network Penetration Tester (PNPT)
- Certified Information Systems Auditor (CISA)
- Certified Information Security Manager (CISM)
- CompTIA Advanced Security Practitioner (CASP+)
- AWS Certified Security Specialty (AWS Security)
- Azure Security Engineer Associate (AZ-500)
- Fortinet Certified in Cybersecurity (FCP)
- Fortinet Certified in Network Security (FCP NSE)
- Cisco Certified Network Associate (CCNA)
Every certification is listed with its issuing body on the credentials page, each independently verifiable on the issuer’s own portal. ISO/IEC 27001 certified information security management system (ISMS).
Want to know who is on your engagement?
The assigned testers are named during scoping and held contractually, not swapped for whoever is free that week.