Team · Application Security Engineer
Midha Ansari
Application security engineer at Dunicot — authorised security assessment, source-code review, and web and API testing.
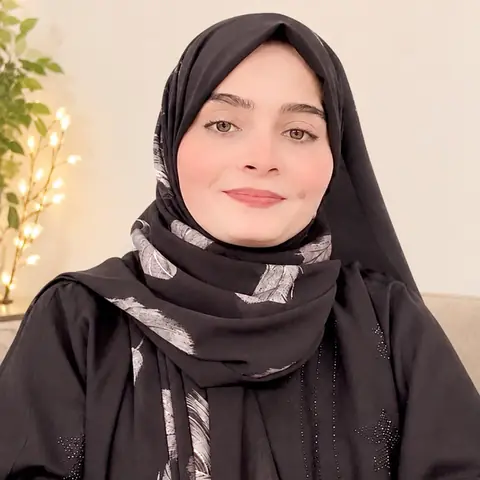
Midha Ansari is an application security engineer at Dunicot. Her work is the authorised assessment of software that clients own or have written permission to test — finding the flaws in web applications and the APIs behind them before someone without that permission does, and reading the source underneath to understand why a flaw exists rather than only that it does.
She holds an MS in Cyber Security from SZABIST University in Karachi, where she is based, and has worked on the firm’s application security engagements since 2024. She works to the same methodology every tester here follows: scanner output is a lead and never a finding, every candidate is reproduced by hand before it is written down, and a report carries only what was demonstrated.
What she works on
Authorised security assessment
Every engagement is scoped and authorised in writing before any testing begins. The target is agreed, the boundaries are agreed, and the techniques that are off the table are agreed, because testing that strays outside its authorisation is not an assessment. Within that scope the brief is simple: behave like the attacker who was never given the rules, and report what actually worked.
Source-code review
Reading the code alongside testing the running application. A black-box test can tell you a request succeeded; the source tells you why the check that should have stopped it was missing, whether the same mistake repeats elsewhere, and what the real fix is. It is the difference between reporting a symptom and reporting a cause, and it is where a one-line finding often turns out to be a pattern.
Web and API testing
Authenticated, multi-role testing of web applications and their APIs, with particular attention to authorisation boundaries — whether one account can reach another’s data, whether a lower-privileged role can call an action it was never shown, and whether the API quietly returns more than the interface ever puts on screen.
Published work
-
The library you shipped without reading
Most of a modern application is code the team never wrote. A dependency scan on this one returned sixty advisories. One of them was exploitable, it was rated moderate, and it was buried four levels down in a package nobody remembered adding.
In brief
- Role
- Application Security Engineer
- At Dunicot
- Since 2024
- Education
- MS Cyber Security, SZABIST University, Karachi
- Based in
- Karachi, Pakistan